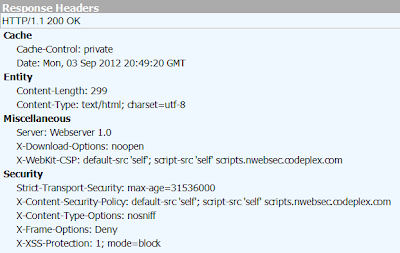
The above content security coverage could presumably be used as a valid configuration for the following webpage. If your application does not require any exterior sources, you would consider implementing a CSP with the directive default-src ‘self’. The default-src directive is used to control the sources from which scripts may be executed. There are varied third celebration tools together with browser extensions and websites that generate these insurance policies. It’s important to notice that after a browser has received and processed the HSTS header, it will automatically redirect any HTTP requests to HTTPS for the required domain and its subdomains.
Utilizing a sha256-value in script-src could be a safety measure when you have specific scripts that need to be executed inline, and you wish to ensure their integrity. It is also attainable to use a SHA256 hash to confirm that a script solely incorporates the anticipated contents. It permits the execution of inline scripts but only for the script-src policy. In script-src, ‘unsafe-inline’ permits the execution of inline scripts. In default-src, ‘unsafe-inline’ allows the utilization of inline scripts and types within the HTML doc. It is essential to notice that nearly all of the above options for default-src apply to script-src and all other directives.
By merely clicking on a suspicious link in an email or chat message, the net site person might by chance give an attacker the flexibility to function their id and access privileges. In a CSRF assault, an attacker uses social engineering methods to handle an authenticated user alexhost.com into performing malicious actions without their consciousness or consent. The Cross-Site Request Forgery (CSRF) attack forces an authenticated person to execute unwanted actions or submit a request on an internet application or website the place they’re currently authenticated. Cross-Site Scripting (XSS) is an attack that permits an attacker to inject malicious executable scripts into the code of a trusted web software or website.
- If the CSP is about to not allow inline scripts, even when the parameters are not sanitized, this can stop the execution of the cross-site scripting assault.
- If you employ Google Analytics, a third-party chat widget, or a CDN for scripts, you should whitelist those origins explicitly.
- This issues most on multi-tenant servers.
- All The Time test adjustments in a staging setting first and roll them out steadily.
- As the name suggests, it exhibits the version details of the ASP .NET framework.
Ideally, all changes made ought to be implemented in a take a look at surroundings earlier than being deployed to manufacturing. The security headers assist shield in opposition to a variety of the attacks which may be executed against an internet site. HTTPS provides encryption for all communication between the consumer and server, which eliminates the potential for a man-in-the-middle (MITM) attack. It can prevent clickjacking assaults, which happen when an attacker methods users into clicking on something apart from what they meant.